APT36 – “Abaris” Deobfuscating VB Dropper
by Robin Dost Subscribe Newsletter I recently discovered a sample attributed to the threat actor APT36 ("Transparent Tribe") on MalwareBazaar....
by Robin Dost Subscribe Newsletter I recently discovered a sample attributed to the threat actor APT36 ("Transparent Tribe") on MalwareBazaar....
APT44 (Sandworm Team) – Quick Facts Type: Advanced Persistent Threat (APT) Aliases: Sandworm, Sandworm Team, Seashell Blizzard, Iron Viking, Telebots, Voodoo Bear, Iridium, FrozenBarents...
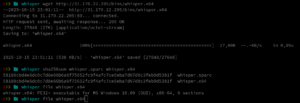
In the past few days I found something fairly interesting in my sandbox. An attacker attempted to install malware, and...
Since I want to dive deeper into reverse engineering, I’ve decided to regularly solve CrackMe challenges from https://crackmes.one; I’ll begin...
APT1 (Comment Crew / Shanghai Group) – Quick Facts Type: Advanced Persistent Threat (APT) Aliases: Comment Crew, Comment Group, Comment...
Dein Open-Source-Tool für Sicherheits-Audits in Jira Server & Data Center In der heutigen Zeit, in der Datenschutz und Compliance oberste...
Malware Name / Type Name: XorDDoS (aka XOR DDoS) Type: Linux Trojan / DDoS botnet (rootkit-capable) Quick Summary First Seen...
Honeypot Details: Type: SSHSoftware used: Cowrie Results We publish partial results in our GitHub repositoryThe repository includes passwords that were...
Here you'll find all of our Cybersecurity related blog entries. Thanks for reading! by @Mr128Bit