GamaWiper Explained: Gamaredon’s “New” Anti-Analysis Weapon
by Robin Dost Subscribe Newsletter After my recent blog posts covering Gamaredon’s ongoing PterodoGraph campaign targeting Ukraine, and following almost...
by Robin Dost Subscribe Newsletter After my recent blog posts covering Gamaredon’s ongoing PterodoGraph campaign targeting Ukraine, and following almost...
I am currently analyzing the recent surge of malware samples exploiting the WinRAR vulnerability CVE-2025-6218. During this research, I found...
by Robin Dost Subscribe Newsletter UPDATE 22.12.2025: Gamaredon updated it's payload delivery infrastructure. You can find more information here.UPDATE 08.01.2026:...
by Robin Dost Subscribe Newsletter If you're interested in reading more about Gamaredon check out my other articles.If you're interested...
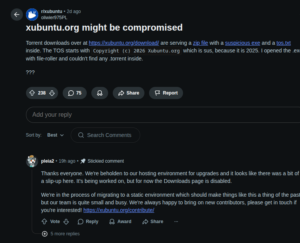
Yesterday I discovered a malware incident that was distributed via the official Xubuntu website.There is already a Reddit post that...
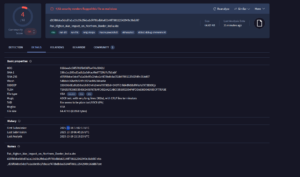
by Robin Dost Subscribe Newsletter I recently discovered a sample attributed to the threat actor APT36 ("Transparent Tribe") on MalwareBazaar....
APT44 (Sandworm Team) – Quick Facts Type: Advanced Persistent Threat (APT) Aliases: Sandworm, Sandworm Team, Seashell Blizzard, Iron Viking, Telebots, Voodoo Bear, Iridium, FrozenBarents...
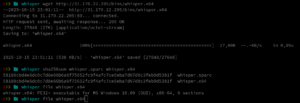
In the past few days I found something fairly interesting in my sandbox. An attacker attempted to install malware, and...
Since I want to dive deeper into reverse engineering, I’ve decided to regularly solve CrackMe challenges from https://crackmes.one; I’ll begin...
APT1 (Comment Crew / Shanghai Group) – Quick Facts Type: Advanced Persistent Threat (APT) Aliases: Comment Crew, Comment Group, Comment...